Home: Northstar Security Advisors
Northstar Security Advisors

A part-time security lead for SaaS companies heading into SOC 2

Mara Chen runs your security program one day a week: policies, audit preparation, and the questionnaires your sales team is waiting on. For companies with 50 to 200 employees.

You get three call times by email within one business day.

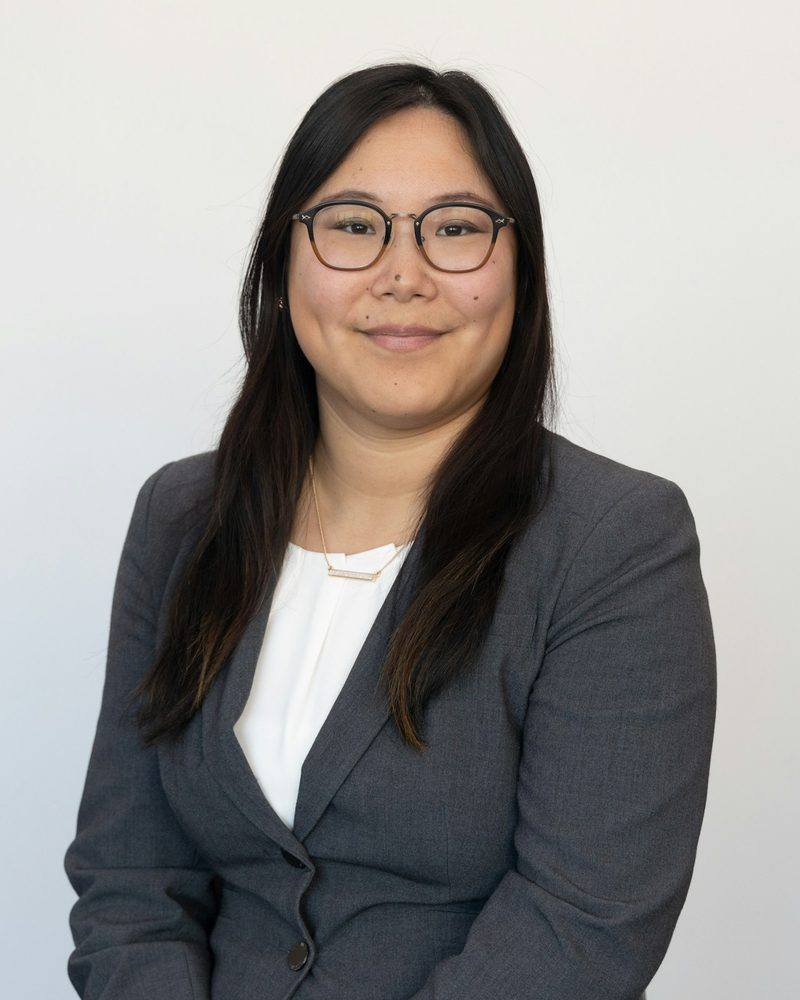
Mara Chen, founder of Northstar Security Advisors, in a grey blazer and glasses
Mara Chen CISSP. Led the first SOC 2 Type II audit at a 140-person software company before starting Northstar in 2021.

Who Northstar works with

SaaS companies with 50 to 200 employees, usually Series A to C, with production on AWS, Google Cloud or Azure and no one on staff whose job is security. Most engagements last 6 to 18 months.

Why companies usually call

  • A prospect sent a 300-question security questionnaire and the deal is waiting on it.
  • A customer asked for your SOC 2 report at renewal.
  • Your board wants a written security program and an owner for it.
  • Your CTO has been running security on the side and is out of hours.

Services

  • Part-time CISO (vCISO)

    Mara joins your leadership meeting every week, owns the security roadmap, and answers customer security questions for you.

    Length
    6 to 18 months
    Price
    $8,000 to $18,000 a month
  • SOC 2 readiness program

    A 90-day program that takes you from no formal compliance work to ready for a SOC 2 Type II audit window.

    Length
    90 days to audit-ready
    Price
    $40,000 to $75,000, fixed after scoping
  • Security assessment

    A 2 to 3 week review of your security against NIST CSF, CIS Controls or SOC 2, delivered as a written report with a ranked list of fixes.

    Length
    2 to 3 weeks
    Price
    $15,000 to $30,000
  • Security awareness training

    Live onboarding sessions, quarterly phishing tests and short monthly scenarios, written for engineering-heavy teams.

    Length
    12 months, renewed yearly
    Price
    $24,000 to $48,000 a year
Three people at a meeting table writing in notebooks, with printed pages spread between them

Your first 30 days

The same opening for every vCISO and SOC 2 client. By day 30 you have two documents and a weekly rhythm.

  1. Day 1

    Kickoff with your CTO and one engineering lead. We agree on scope and who owns what.

  2. Days 2 to 10

    Mara reads your existing docs, maps where customer data lives, and interviews 3 to 5 people.

  3. Day 14

    You receive the Discovery Document: scope, current state, and the gaps that matter for your audit.

  4. Day 21

    You receive a 12-month roadmap with owners, dates and a tooling budget.

  5. Day 30

    Weekly cadence starts: one standing meeting, policy drafts in review, compliance platform connected.

The Northstar Maturity Framework

Every engagement runs through the same five phases. Each phase ends with a document you keep.

  1. 1Discovery 2 weeks

    Data-flow map, frameworks in scope, and where your program stands today.

    You keep: Discovery Document, 6 to 12 pages

  2. 2Roadmap 1 week

    Prioritized work with owners and a budget, reviewed with your leadership team.

    You keep: 12-month roadmap

  3. 3Build 8 to 16 weeks

    Policies written, controls configured, and your compliance platform collecting evidence.

    You keep: Policies, controls and evidence collection in place

  4. 4Validate 2 to 4 weeks

    Tabletop exercise, penetration test coordination, and a mock audit.

    You keep: Readiness report and gap-closure plan

  5. 5Operate Ongoing

    Weekly leadership meeting, questionnaire answers, and incident response readiness.

    You keep: Quarterly security review

Sample case studyFictional client

From stalled deals to a clean SOC 2 Type II report in nine months

Ledgerline had three enterprise contracts waiting on a SOC 2 report. Mara joined one day a week, ran the readiness program, and the report came back clean nine months after kickoff. All three contracts were signed within six weeks of it.

Read the Ledgerline case study
Client
Ledgerline, reconciliation software for finance teams
Size
90 employees, Series B
Engagement
8-month vCISO engagement with SOC 2 readiness
Months to Type II report
9
Policies written
14
Exceptions in the report
0

How Mara runs an engagement

“Mara sat in our Tuesday leadership meeting for eight months. By the time the auditor arrived, our engineers were answering the control questions themselves.”

Head of Engineering, Ledgerline (sample client) Demo
Mara runs every engagement herself.
The person on the fit call is the person in your weekly meeting and the person who writes your policies. Northstar takes on at most six clients at a time.
Same five phases every time.
Every engagement follows the Northstar Maturity Framework, so you know on day one what you will receive in week two and week three.
Your engineers keep their sprints.
Mara spent six years inside engineering teams. Controls are mapped to the process you already run, and new work goes into your ticket tracker with an estimate.
Everything stays in your systems.
Policies live in your wiki, evidence in your compliance platform, tasks in your tracker. Nothing is locked in a consultant portal.

Common questions

Anything else goes on the fit call, or email [email protected].

A vCISO engagement is $8,000 to $18,000 a month depending on scope. A SOC 2 readiness program is $40,000 to $75,000 for 90 days. An assessment is $15,000 to $30,000. You get a written scope and a fixed price after the fit call, before anything is signed.

90 days from kickoff to audit-ready if you already have cloud infrastructure, source control and single sign-on in place. Starting from scratch takes 4 to 5 months. The audit window itself adds 3 to 12 months for Type II, set by you and your auditor.

Northstar works with SaaS companies under 200 employees, including B2B fintech. Hardware, government contractors and companies over 250 people get a referral to a firm that specializes in them.

It takes 30 minutes. Mara asks what is driving the work, such as a deal, an audit date, an incident or a board request. If Northstar fits, you get a written scope and price within three business days. If it does not, she names a firm that does.

Mara Chen, on every engagement. Northstar does not subcontract. Penetration tests are run by an outside firm you contract directly, and Mara coordinates them.

Yes. When a client is ready, Mara helps write the job description, sits in on interviews, and hands over the program. The engagement has a 30-day exit clause for this.

Most clients move to a one-day-a-month retainer covering quarterly reviews, preparation for the annual audit, and incident response readiness.

Book a 30-minute fit call with Mara.

Tell her what is driving the work. If Northstar fits, you get a written scope and price within three business days.

Book a 30-minute fit call